

Quick answer: AI agents vs agentic AI
In the vendor documentation cited below, an AI agent is a software system that uses a model to pursue a goal and take actions through tools. Agentic AI, in the same documentation, is the broader approach of building systems that plan, act and adapt with a degree of autonomy, often by coordinating several agents. The sources draw the line between the two in different places, so each definition below is credited to its author.
The definitions in this article come from IBM, Google Cloud, AWS, Anthropic and OpenAI documentation and from the 2025 taxonomy paper by Sapkota and co-authors. All of them were read in October 2026.
What an AI agent is
According to Google Cloud, AI agents are software systems that use AI to pursue goals and complete tasks on behalf of users. They show reasoning, planning and memory, and they have a level of autonomy to make decisions, learn and adapt. According to AWS, an AI agent is a software program that interacts with its environment, collects data and uses that data to perform self-directed tasks that meet predetermined goals. Humans set the goals, and the agent chooses the actions. According to OpenAI's 'A practical guide to building agents', agents are systems that independently accomplish tasks on the user's behalf. OpenAI says simple chatbots, single-turn LLMs or sentiment classifiers that do not control workflow execution are not agents. That makes three definitions from three vendors.
According to OpenAI's practical guide, an agent "in its most fundamental form" has three core components. A model powers reasoning and decision-making, tools (external functions or APIs) let it take action, and instructions (the guidelines and guardrails) define how it behaves. According to Google Cloud, an agent is built from a persona, memory (short-term, long-term, consensus and episodic), tools and a model. Of these two lists, only Google Cloud's includes memory, so memory is not a given for every agent.
Take refund approval as an example. OpenAI cites it as complex decision-making suited to agents. The model reads the request and the instructions carry the policy. Tools look up the order, so the agent can act or hand off to a person.
What agentic AI is
According to IBM, agentic AI is an artificial intelligence system that can accomplish a specific goal with limited supervision. In a multiagent system, each agent performs a specific subtask while AI orchestration coordinates their efforts. IBM calls autonomy the most important advance of agentic systems. Such systems perform tasks without constant human oversight, maintain long-term goals, manage multistep problem-solving tasks and track progress over time.
"The most important advancement of agentic systems is that they allow for autonomy to perform tasks without constant human oversight. Agentic systems can maintain long-term goals, manage multistep problem-solving tasks and track progress over time."
Source: ibm.com
According to AWS, agentic AI is an autonomous AI system that can act independently to achieve pre-determined goals. AWS describes it as proactive, able to perform complex tasks without constant human oversight. It counts two setups: a single agent that handles all tasks sequentially, or multiple agents that collaborate to break complex workflows into smaller segments.
The 2025 review 'AI Agents vs. Agentic AI: A Conceptual Taxonomy, Applications and Challenges' by Sapkota, Roumeliotis and Karkee (Information Fusion; arXiv 2505.10468) draws a sharper line. According to Sapkota et al.'s 2025 review, AI agents are modular systems driven and enabled by LLMs and LIMs for task-specific automation. Agentic AI, in the paper's framing, marks a paradigm shift defined by multi-agent collaboration, dynamic task decomposition, persistent memory and coordinated autonomy.
The sources disagree on the boundary. AWS counts a single agent as agentic AI, and according to IBM a single AI agent performs task decomposition. Anthropic puts fully autonomous systems and prescriptive implementations that follow predefined workflows under its own umbrella term, agentic systems.
How AI agents fit inside an agentic system
According to IBM, agentic AI consists of AI agents, models that mimic human decision-making to solve problems in real time. AWS says it typically builds on several hyperspecialized agents that coordinate and hand off tasks as needed. The coordination layer has work of its own. In IBM's description, AI orchestration platforms track progress toward task completion, manage resource usage, monitor data flow and memory and handle failure events. IBM adds that a conductor model supervising simpler agents suits sequential workflows but is vulnerable to bottlenecks.
AI agents vs agentic AI at a glance
| Aspect | AI agent | Agentic AI |
|---|---|---|
| Scope | Task-specific automation | Complex, multi-step goals |
| Autonomy | Self-directed within a goal | Coordinated autonomy |
| Planning | Optional for simple tasks | Dynamic task decomposition |
| Memory | Varies by source | Persistent memory |
| Coordination | Single, task-specific agent | Multi-agent collaboration |
| Example (Sapkota et al.) | Customer support, scheduling | Research automation |
The table combines the Sapkota et al. abstract with IBM, Google Cloud and AWS documentation. IBM says an AI agent performs task decomposition, and that for simple tasks planning is not a necessary step. Google Cloud says an agent is generally equipped with long-term memory, and AWS also counts one agent working through tasks in sequence as agentic AI. So read the planning, memory and coordination rows as the paper's view rather than a settled rule.
Initiative and learning
A common shorthand says AI agents wait for a prompt while agentic AI takes the initiative. Google Cloud's comparison table draws the line elsewhere: it calls AI agents proactive and goal-oriented, AI assistants reactive to user requests and bots reactive to triggers or commands, with predefined rules and limited learning. By that table, a tool that acts only when asked is an assistant or a bot. AWS contrasts agentic AI with traditional systems that respond only when triggered, and says multi-agent AI typically spreads learning across agents through communal memory layers.
Workflows vs agents: a practical test
Anthropic offers the most usable dividing line. According to Anthropic's 'Building effective agents' (December 2024), workflows are systems where LLMs and tools are orchestrated through predefined code paths. Agents are systems where LLMs dynamically direct their own processes and tool usage, keeping control over how they accomplish tasks. Anthropic adds that agents are typically just LLMs using tools based on environmental feedback in a loop. It is common to add stopping conditions, such as a maximum number of iterations.
Workflows offer predictability and consistency for well-defined tasks. Agents suit open-ended problems where the number of steps is difficult or impossible to predict and a fixed path cannot be hardcoded. Anthropic recommends finding the simplest solution possible and adding complexity only when needed, which may mean not building agentic systems at all. For many applications, it says, optimizing single LLM calls with retrieval and in-context examples is usually enough.
To apply the test, write the process out step by step. If you can draw every branch in advance, build a workflow. If the next step depends on what the system finds, such as the content of a free-text customer message, an agent step may be justified. OpenAI makes a similar point: without complex decisions, hard-to-maintain rules or heavy unstructured data, a deterministic solution may suffice.
One more question helps: can a person check the output faster than they could do the job? In r/AI_Agents threads, people who use agents at work describe the clearest gains on narrow, repeated jobs such as status reports, first-line support tickets and first drafts. They report misses on work that needs judgment across a lot of context, such as ranking a backlog or reviewing a large code change. As one of them put it: "what still doesn't work is anything needing real judgment across a long context."
Examples of each
- Support agent (AI agent). Anthropic describes customer support as a natural fit for more open-ended agents. The setup pairs a chatbot interface with tools that pull customer data, order history and knowledge base articles. Actions such as issuing refunds or updating tickets can be handled programmatically.
- Coding agent (AI agent). Anthropic cites its own coding agent that resolves SWE-bench tasks, which involve edits to many files based on a task description.
- Computer-use agent (AI agent). In Anthropic's 'computer use' reference implementation, Claude uses a computer to accomplish tasks. In OpenAI's July 2025 launch post, which OpenAI now marks as outdated, ChatGPT agent was described as thinking and acting. The post said it chose from a toolbox of agentic skills to complete tasks using its own computer and asked permission before taking actions of consequence.
- Multi-agent research system (agentic AI). Anthropic defines a multi-agent system as multiple agents (LLMs autonomously using tools in a loop) working together. In its Research feature, a lead agent coordinates the process, delegates to specialized subagents that run in parallel and saves its plan to memory to persist the context.
- Orchestrated operations flow (agentic AI). OpenAI's guide describes a decentralized pattern in which agents operate as peers and hand off tasks according to their specializations. In its example, a triage agent passes a question about a recent purchase to an order-management agent.
- The paper's own mapping (both). In the Sapkota et al. taxonomy (2025 review, abstract), AI agents map to customer support, scheduling and data summarization. Agentic AI maps to research automation, robotic coordination and medical decision support.
The support agent and the orchestrated operations flow handle the same kind of request, a customer asking about an order. The first keeps it inside one agent with several tools; the second has a triage agent hand it to a specialist. Which of the two counts as agentic AI depends on whose definition you use, as the sources above show.
Where generative AI fits
Generative AI produces content on request. IBM's agentic AI FAQ uses ChatGPT as its example of a generative AI model and says such a model might produce text, images or code. In IBM's account, an agentic AI system can use that generated content to complete complex tasks autonomously by calling external tools. The Sapkota et al. review positions generative AI as the precursor that provides the foundation. In the paper's view, AI agents advance through tool integration, prompt engineering and reasoning enhancements.
Put together, these form layers. A model generates content. An AI agent wraps a model with tools and a goal. Anthropic calls an LLM enhanced with retrieval, tools and memory the basic building block of agentic systems. Agentic AI then coordinates one or more such agents with more autonomy and less supervision.
Risks and controls
OWASP's Top 10 for LLM applications (2025 edition) lists Excessive Agency as LLM06:2025. It is the vulnerability that enables damaging actions in response to unexpected, ambiguous or manipulated LLM outputs, whatever causes the LLM to malfunction. OWASP names three typical root causes: excessive functionality, excessive permissions and excessive autonomy. Among the triggers it lists prompt injection, including injection from a malicious or compromised peer agent in multi-agent systems.
"The autonomous nature of agents means higher costs, and the potential for compounding errors. We recommend extensive testing in sandboxed environments, along with the appropriate guardrails."
Source: anthropic.com
Start with least privilege. OWASP recommends limiting the tools an agent may call, and the permissions those tools hold on other systems, to the minimum necessary. OpenAI's guide suggests rating each tool's risk as low, medium or high. The rating rests on read-only versus write access, reversibility, required account permissions and financial impact. For high-impact actions, OWASP recommends human-in-the-loop approval before they are taken.
Tie each approval to the exact action. Show the approver what will actually run, such as the recipient, the amount and the final text, rather than the agent's summary of it. Ask again if any of it changes before it runs, and do not let a later run reuse an old approval. One user on r/AI_Agents described what goes wrong otherwise: "Someone approves a reply, then the agent edits the price or delivery promise before it goes out. The person approved a different message."
Give each agent its own identity and access permissions. IBM's agentic AI FAQ says unique agent identity, provided by platforms such as IBM Verify, helps minimize the security risks that come with integration.
A rule written into the agent's prompt guides it, but prompt injection or a misread task can push it past that rule. Put the hard limits where the model cannot argue with them: in the tools it can call and in what its own account or API key may do, such as read-only access or a spending limit. Rules that live only in an app's screens, like a field hidden on a form, do not stop an agent that works through an API either. One user on r/AI_Agents put it this way: "prompt instructions are not governance, they're a suggestion the model usually follows."
Then make the agent's activity visible. OWASP notes that logging and monitoring tool activity will not prevent Excessive Agency but can limit the damage. Anthropic warns that agent autonomy means higher costs and the potential for compounding errors. It recommends extensive testing in sandboxed environments with appropriate guardrails. Anthropic also advises starting evaluation right away with small-scale tests on a few examples, and says full production tracing let it diagnose why agents failed.
A clean log is not proof that the work got done. For any write that matters, check the result in the system it was meant to change, for example by reading the record back. Treat a call that timed out as unknown rather than failed, since retrying it blindly can create a duplicate. One user on r/AI_Agents put the risk this way: "An agent that quietly lost inbox access will happily log 'nothing to do' forever, and your audit trail will back it up."
A system of several agents adds failure modes of its own. IBM warns that traffic jams, bottlenecks and resource conflicts between agents can cascade. AWS notes that false information one model relays to the other agents can spread into the final output. Because these systems work with minimal human intervention, AWS also tells developers to build in traceability, so errors can be traced to their causes.
How to start: from one agent to an agentic system
- Pick one process. OpenAI advises prioritizing workflows that have resisted automation, especially those with complex decision-making, rules that are hard to maintain or heavy reliance on unstructured data. If none of that applies, a deterministic solution may suffice.
- Build it as a workflow first. Anthropic advises finding the simplest solution possible. For many applications, a single LLM call with retrieval and in-context examples is usually enough.
- Add one agent step with limited tools. Give it only the tools that step needs, rate each tool's risk, and set a stopping condition such as a maximum number of iterations.
- Add human review. Route consequential or hard-to-reverse actions, such as refunds or writes to customer records, to a person for approval before they run.
- Measure. Test on a handful of real examples right away, trace every run, and compare the agent step with the workflow it replaced on accuracy and cost.
- Expand to several agents only when needed. OpenAI recommends maximizing a single agent's capabilities first, starting small and validating with real users. As Anthropic wrote in June 2025, domains where all agents must share the same context, or with many dependencies between agents, were not a good fit for multi-agent systems at the time. Most coding tasks, it added, involve fewer truly parallelizable tasks than research.
Anthropic's June 2025 post also names where several agents do pay off: valuable tasks with heavy parallelization, information that exceeds a single context window and work with many complex tools. The same post warns that these setups burn through tokens fast, so the task must be valuable enough to pay for the extra performance.
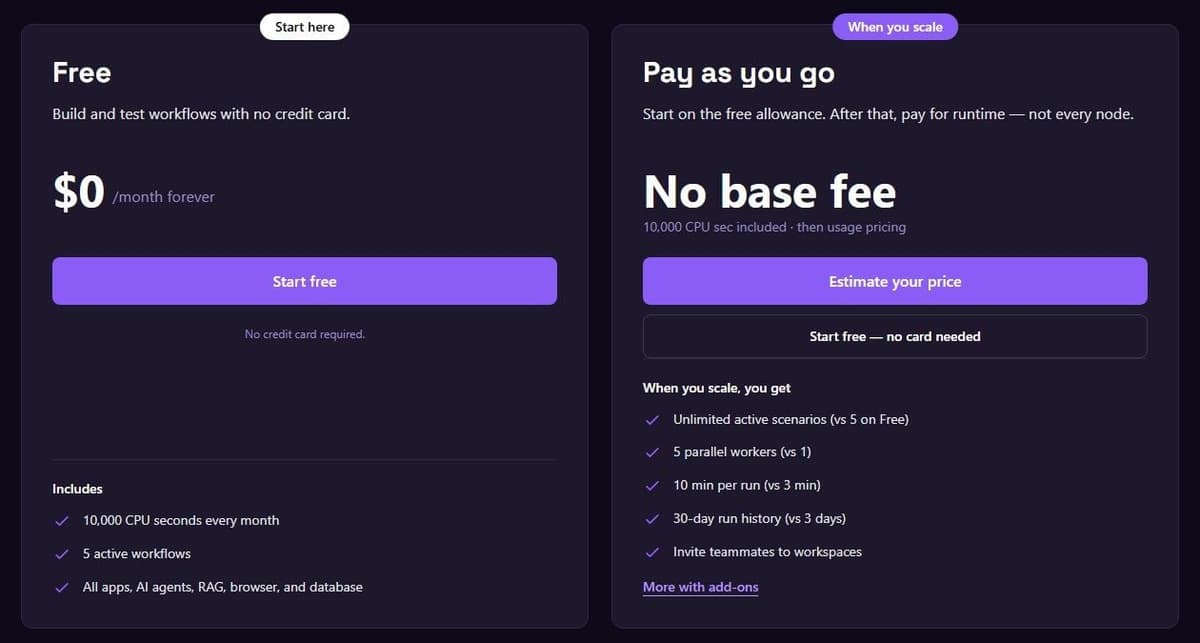
If you want to try this path on Latenode, its own pages state the following as of September 2026. The pricing page lists a visual drag-and-drop builder, an AI Agent builder for business processes and 335+ LLM models (GPT, Claude, Gemini and others) available under one subscription. Latenode's site also describes custom JavaScript support through JS nodes. Billing counts workflow runtime in CPU seconds (runs x average seconds), not operations or steps. The first 10,000 CPU seconds are free every month on both plans, Free and Pay as you go. Pay as you go has no base fee, and usage beyond that allowance costs $0.00012 per CPU second in the 10,001-100,000 bracket. Cost depends on run duration, so it is not directly comparable to other platforms' tasks or credits. Nodes that call paid external providers are marked with a $ icon. They use optional PnP tokens at $1 per token by actual provider usage, billed in addition to runtime. Judge it against the process you picked in step 1, not against a feature checklist.